
OCPT – Ocsaly Certified Penetration Tester

CERTIFICATION // Ethical Hacking // OCPT

Ocsaly Certified Penetration Tester

OPERATORS TRAINED : 580.000+

Master Professional Infrastructure Assessment Through Practical Execution.

Operational Dominance

The Full-Spectrum Certification Track (Phases A-C)
Phase 1
>> PHASE 01 : RECONNAISSANCE

Intelligence & Architecture

The Foundation. Before you strike, you must see. Master the physics of the network, dissect the OSI model, and execute stealth target acquisition with Nmap and Wireshark.
Phase 2
>> PHASE 02 : WEAPONIZATION

Ethical Hacking & Prof Bug Bounty

The Arsenal. Manual hacking is too slow. Transition to Systems Operations and master the "Builder/Breaker" trilogy: Bash, Python, and PowerShell to automate your kill chain.

Phase 3
>> PHASE 03 : EXPLOITATION

Binary Engineering & Dev

The Apex. Leave the script kiddies behind. Enter the world of Memory Corruption. Use C and Assembly to reverse engineer binaries and hand-craft custom shellcode.

[ OPERATIONAL_CREDENTIAL ]
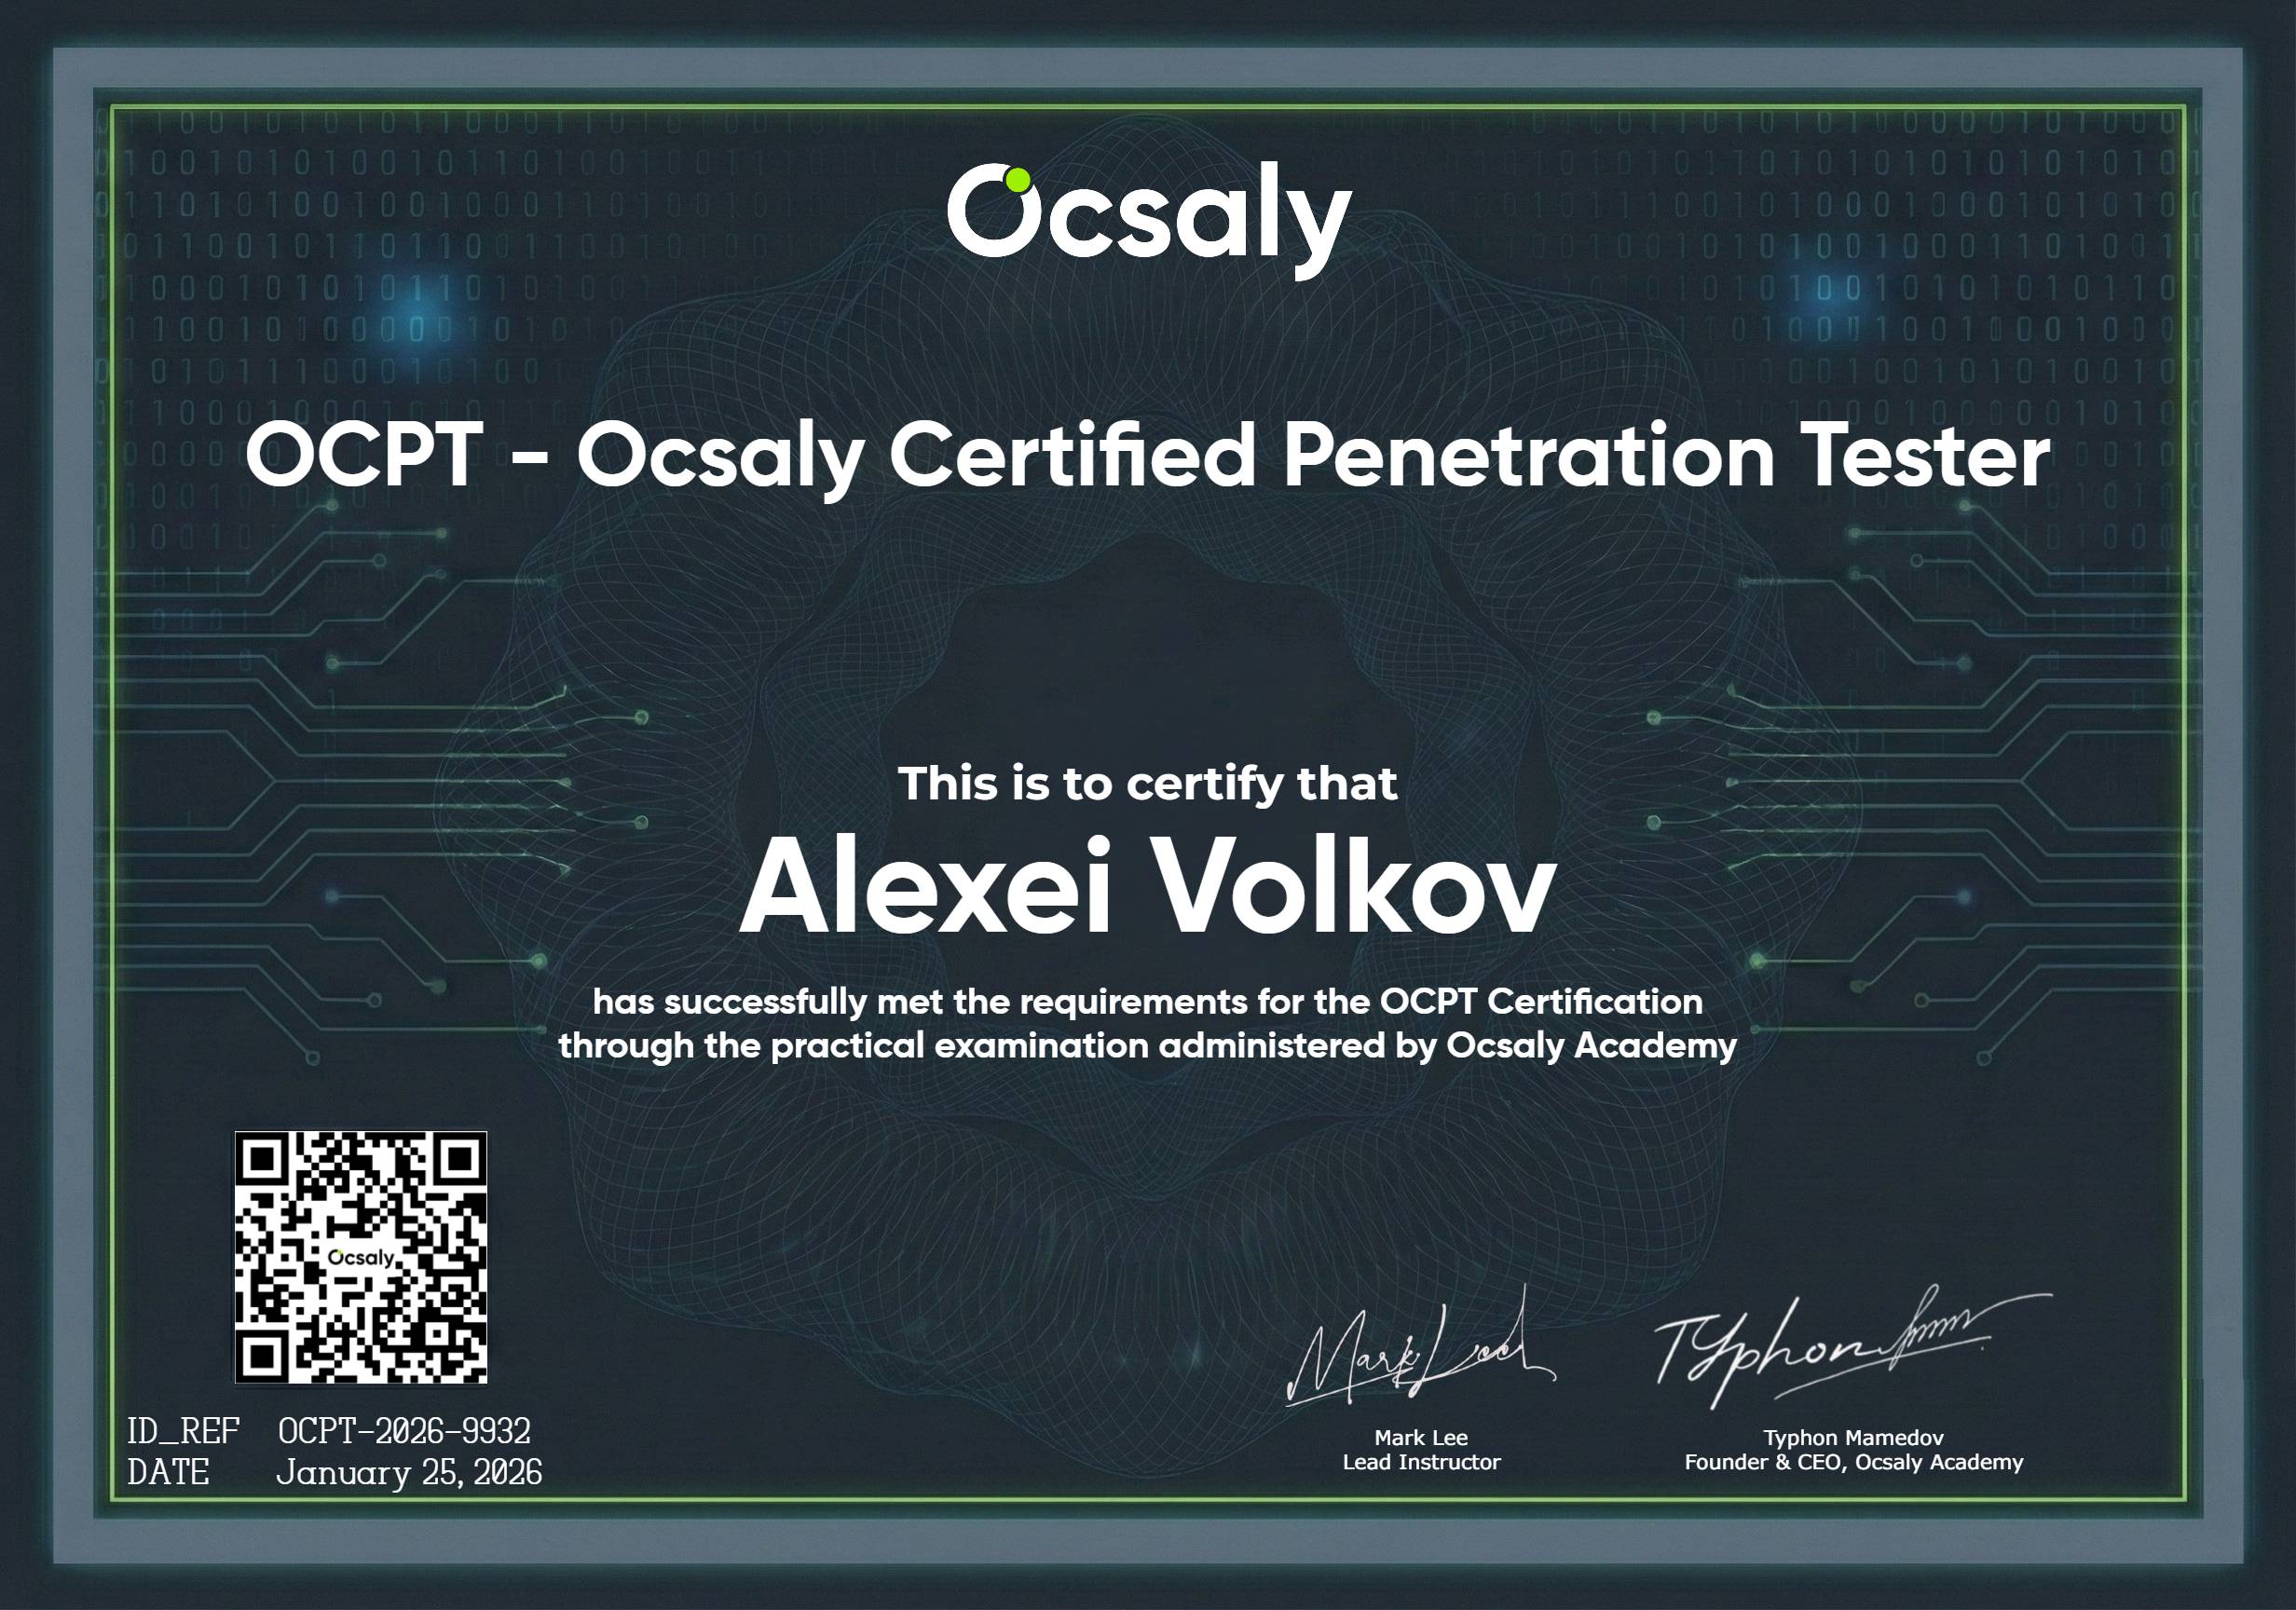
OCPT Certificate Template
VERIFIABLE PRACTITIONER STATUS
STANDARD VALUE: $646.00
$ 199 .00 / BUNDLE ACCESS
[ ENROLL IN OCPT PROGRAM NOW ]

// INSTANT ACCESS GRANTED

[ INCLUDED_MODULES ]

  • ✓ OCPT-A: Reconnaissance
    57+ Hours ($149 Value)
  • ✓ OCPT-B: Weaponization
    20+ Hours ($149 Value)
  • ✓ OCPT-C: Exploit Dev
    25+ Hours ($149 Value)
  • FINAL EXAM: 24h Practical
[ MISSION_READY_STATUS ]

Professional Career Outcomes

01

Red Team Operator

Execute advanced adversarial simulations and multi-stage kill chains.

02

Threat Hunter

Analyze post-compromise artifacts to identify and neutralize active breaches.

03

Infrastructure Specialist

Secure critical national infrastructure and government-grade systems.

// VERIFIED_PRACTITIONER_DEBRIEFS

Operational Validation

REF: OCPT-7721

"The memory corruption module in Phase C was the first time x64 registers actually clicked. The lab environment forced a logic shift that my CS degree never touched."

Marcus Thorne L2 SOC Analyst
[ VERIFIED ]
REF: OCPT-4409

"Most certifications are multiple choice. Ocsaly is a 24-hour siege. You don't just learn tools; you learn why tools fail and how to engineer your own custom wrappers."

Elena Rodriguez Red Team Operator
[ VERIFIED ]
REF: OCPT-1102

"The Phase B lateral movement labs are brutal. Pivoting through three subnets with restricted tooling finally gave me the confidence to handle real-world infrastructure."

David Chen Security Engineer
[ VERIFIED ]
REF: OCPT-8832

"Ocsaly doesn't hold your hand. The troubleshooting required during the Phase A reconnaissance forced me to understand the underlying protocols, not just the Nmap flags."

Sarah Jenkins Penetration Tester
[ VERIFIED ]
REF: OCPT-2219

"The institutional focus on manual exploitation logic over automated scripts is what sets this apart. It’s the difference between being a tool-user and being an operator."

Julian Vane Threat Hunter
[ VERIFIED ]
REF: OCPT-5541

"24 hours for the exam seemed like a lot until the clock started. The reporting requirements alone forced me to think like a consultant, not just a technical tinkerer."

Aarav Patel Cybersecurity Consultant
[ VERIFIED ]
// SECTOR_STATUS: ACTIVE // MISSION_PAYLOAD: 150+ HOURS // AUTH_LEVEL: PRACTITIONER

Operational Inventory & Certification

OCPT-A Reconnaissance 57 HOURS

OCPT-A: RECONNAISSANCE & INTEL

$149.00

CORES: CPU Architecture, x86/x64 Logic, Memory Registers (EAX, ESP, EIP), Ghidra Reverse Engineering, Binary Analysis, Logic Gates.
NETWORK: OSI Model Dissection, TCP/IP Handshakes, ICMP, DNS, SMB Enumeration, SMTP, FTP Dissection.
TOOLKIT: Nmap (Stealth Scanning, NSE Scripting), Wireshark (Packet Dissection, PCAP Analysis), TCPDump, Netcat, Google Dorking, OSINT Frameworks.

OCPT-B Weaponization 21+ HOURS

OCPT-B: WEAPONIZATION & SCRIPTING

$149.00

SYSTEMS: Linux Kernel, Bash Scripting, Cron Jobs, Permissions, SSH/RDP Tunneling, Privilege Escalation Foundations.
AUTOMATION: Python Offensive Dev, PowerShell Empire, Socket Programming, Custom Exploit Wrappers, Multi-Threading Scanners, API Interception.
CRYPTO: Hash Cracking (John the Ripper, Hashcat), Rainbow Tables, MD5, SHA-256, Bcrypt, Salt Dissection, Brute-Forcing Workflows.

OCPT-C Binary Exploitation 20+ HOURS

OCPT-C: BINARY EXPLOITATION

$149.00

DEVELOPMENT: C Programming, x86 Assembly (ASM), Compiled Binary Reversing, Stack vs Heap Analysis, Endianness.
EXPLOITS: Buffer Overflows, Fuzzing, Offset Calculation, Bad Character Filtering, JMP ESP, EIP Overwrite, NOP Sleds.
ENGINEERING: Shellcode Development, Payload Injection, Reverse Shells, Bypassing ASLR/DEP Foundations, Malware Logic & Persistence.

OCPT Official Certification

OCPT PRACTITIONER CERTIFICATION & EXAM

$199.00

EXAM: 24-Hour Hands-On Practical Examination in Private Lab Environment. Full Operational Report Required.
CREDENTIAL: Verifiable Digital ID, Permanent Record of Practitioner Status, High-Resolution PDF/Physical Credential Access.
VALIDATION: Cryptographically Signed Verification Code for Employer Authentication.

[ BUNDLE_AUTHORIZATION ]

Technical Curriculum (A+B+C) $447.00
Certification & Exam Fee $199.00
COMBINED RETAIL VALUE $646.00
BUNDLE OPTIMIZATION - $447.00 SAVED
FINAL ACCESS FEE:
$199.00
  • ✓ Full Lifetime Access (All 3 Modules)
  • ✓ 150+ Hours of Technical Video Content
  • ✓ Official Certification & Exam Attempt
  • ✓ Practitioner-Grade Operational Resources
INITIALIZE FULL ACCESS >>
PRACTITIONER
// INSTITUTIONAL_VERDICT

THE PRACTITIONER STANDARD

The OCPT is not a participatory award. It is a practitioner-grade credential earned through the manual execution of exploitation logic. When you hold this ID, you carry a verified history of Operational Dominance.

INFRASTRUCTURE Private Live-Fire Labs
VALIDATION 24-Hour Practical Warfare
STATUS Permanent Registry Entry

Admission is the first step. The exam is the final filter.
Welcome to the Academy.

// OPERATIONAL_DATA_QUERY

Operational FAQs

Is this track beginner-friendly? +
Ocsaly does not provide "intro to computers." We expect a working knowledge of the Linux CLI and networking fundamentals. We bridge the gap from student to operator.
How long is the OCPT program? +
The full track (Phases A-C) contains 150+ hours of technical content, plus unlimited hours in the private labs.
Are the modules updated? +
Yes. Exploitation logic evolves. All practitioners get lifetime access to curriculum updates within their purchased modules.
How does OCPT compare to academic certifications? +
Academia focuses on memorizing definitions. OCPT focuses on execution. You don't memorize the OSI model; you dissect it.
What is the "Builder/Breaker" methodology? +
We teach you to build the tools (Python/Bash/C) before we teach you to break the systems. An operator who understands the code is superior to a script-kiddie.
Do I need a Computer Science degree? +
No. We value logic and tradecraft over paper credentials. If you can pass the labs, you are mission-ready.
Is the content mostly video or text? +
It is a hybrid of high-density technical video walkthroughs and manual lab guides designed for active execution.
What language is the course conducted in? +
Standard operational English.
Can I buy modules individually? +
Yes, but the Bundle Optimization saves you $447.00 and provides the full kill-chain context.
What is the focus of Phase C? +
Advanced Binary Exploitation. You move from network attacks to memory corruption, hand-crafting shellcode in C and Assembly.
How does the OCPT Exam work? +
It is a 24-hour practical siege in an isolated network. You have one goal: achieve administrative control over the target infrastructure.
Is there a written report requirement? +
Yes. After the 24-hour exploitation window, you have an additional 24 hours to submit a professional-grade technical report.
What is the passing score? +
Grading is based on objectives met and the quality of the report. It is a binary result: Certified or Not.
How long does grading take? +
Our institutional board audits every report manually. Expect a verdict within 7-10 business days.
What happens if I fail the exam? +
There is a 14-day mandatory cool-down period. Use this time to return to the labs and fix your logic flaws.
Are the exams proctored? +
We use automated session logging and human audit of your technical reports to ensure institutional integrity.
Is the certification permanent? +
Yes. Once you are entered into the registry, your practitioner status does not expire.
Can I use automated scanners in the exam? +
You can use any tool in your arsenal, but the exam is designed to break automated tools. Manual logic is the only way to succeed.
Do I get a physical certificate? +
Every graduate gets a high-resolution digital credential and access to order a high-quality physical institutional certificate.
How do I start the exam? +
You schedule your mission window via the Practitioner Dashboard when you feel your tradecraft is ready.
How do I access the labs? +
Secure VPN. We provide OpenVPN configuration files for direct access to our private VLAN infrastructure.
Are the labs shared with other students? +
No. Each practitioner is assigned private instances. Your progress and exploits will not be interfered with by others.
What are the hardware requirements? +
A mid-range machine capable of running a Kali or Parrot VM. If you can run Ghidra and Wireshark, you're fine.
Is lab access 24/7? +
Yes. Our infrastructure is high-availability. You train on your own schedule.
Can I reset the lab machines? +
Yes. You have full control to revert or reboot your target machines via the dashboard if your exploit crashes a service.
Do the labs expire? +
Bundle access includes 90 days of dedicated lab time per module. Extensions are available if you need more time in the trenches.
Is there a web-based console? +
No. Professional operators work from their own machines. We expect you to maintain your own attack environment.
What happens if the labs go down? +
Technical support is active. If our infrastructure fails, we credit your account with additional lab time.
Are the lab targets real machines? +
Yes. We do not use simulations. You are attacking real Windows and Linux targets with real vulnerabilities.
Can I access labs from multiple IPs? +
For security reasons, VPN access is restricted to one concurrent connection per practitioner.
How do employers verify my status? +
Every practitioner is issued a unique ID. Employers can enter this ID into our secure portal to verify your certification and exam date.
Is Ocsaly recognized by the industry? +
Ocsaly is a "Proof of Work" academy. We are recognized by technical leads who value practical skill over multiple-choice theory.
Is there a community for graduates? +
Yes. Verified practitioners gain access to the secure Ocsaly Discord—a private network for tradecraft discussion and job leads.
Does Ocsaly offer job placement? +
We don't "place" you. We provide the technical pedigree that makes you the top 1% of candidates. Our registry is often audited by partner recruiters.
Can I add this to my LinkedIn? +
Yes. We provide verifiable digital badges that integrate directly with professional social networks.
Are there networking opportunities? +
The Practitioner Registry allows you to opt-in to be discoverable by other certified operators and institutional partners.
What roles can I apply for after OCPT? +
L2 SOC Analyst, Penetration Tester, Red Team Operator, and Security Consultant.
Is there post-certification support? +
Our alumni logs remain open. You retain access to the community and updated course materials indefinitely.
How do I get my ID number? +
Your REF ID is generated the moment you pass the OCPT practical exam and is etched into the institutional registry.
Why choose Ocsaly over a Bootcamp? +
Bootcamps are for-profit factories. Ocsaly is a practitioner academy. We focus on the tradecraft that survives a real engagement.
// OPERATIONAL_DEPLOYMENT

Sector Integration

OCPT Practitioners are currently active and validated within the following high-stakes environments:

â–ˆ
National Infrastructure SCADA & Gov-Grade Systems
â–ˆ
Tier-1 Finance Banking & High-Freq Trading Networks
â–ˆ
Aerospace & Defense Intelligence Research & Simulations
â–ˆ
Fortune 500 IR Global Incident Response Teams
// PRE_FLIGHT_CHECKLIST

Mission Requirements

COMPONENT MINIMUM SPECIFICATION RECOMMENDED PROFILE
Operating System Linux (Kali/Parrot) or Win10+ Dedicated Hacking VM
Hardware (RAM) 4GB Total System RAM 16GB+ Optimized for VMs
CPU Logic Quad-Core 2.0GHz+ Hex-Core+ x64 Architecture
Connectivity 5Mbps (OpenVPN Compatible) 20Mbps+ (Low Latency Labs)
INSTITUTIONAL_STANDARD:

If the technical depth of the OCPT does not meet the standards outlined in this dossier within 7 days, we provide a no-friction tuition reversal. We only train those who find value in our logic.

// FINAL_INVENTORY_AUDIT

Curriculum Valuation

OCPT-A: RECONNAISSANCE & INTEL $149.00
OCPT-B: WEAPONIZATION & SCRIPTING $149.00
OCPT-C: BINARY EXPLOITATION $149.00
OCPT PRACTITIONER EXAM & CERTIFICATION $199.00
COMBINED RETAIL VALUE $646.00
INSTITUTIONAL_SAVINGS -$447.00
AUTHORIZED BUNDLE ACCESS
$199.00

// LIFETIME ACCESS. ALL MODULES. ONE CREDENTIAL.

INITIALIZE OCPT ENGAGEMENT CRYPTOGRAPHICALLY SECURED CHECKOUT