
CERTIFICATION // Digital Forensics // OCFI
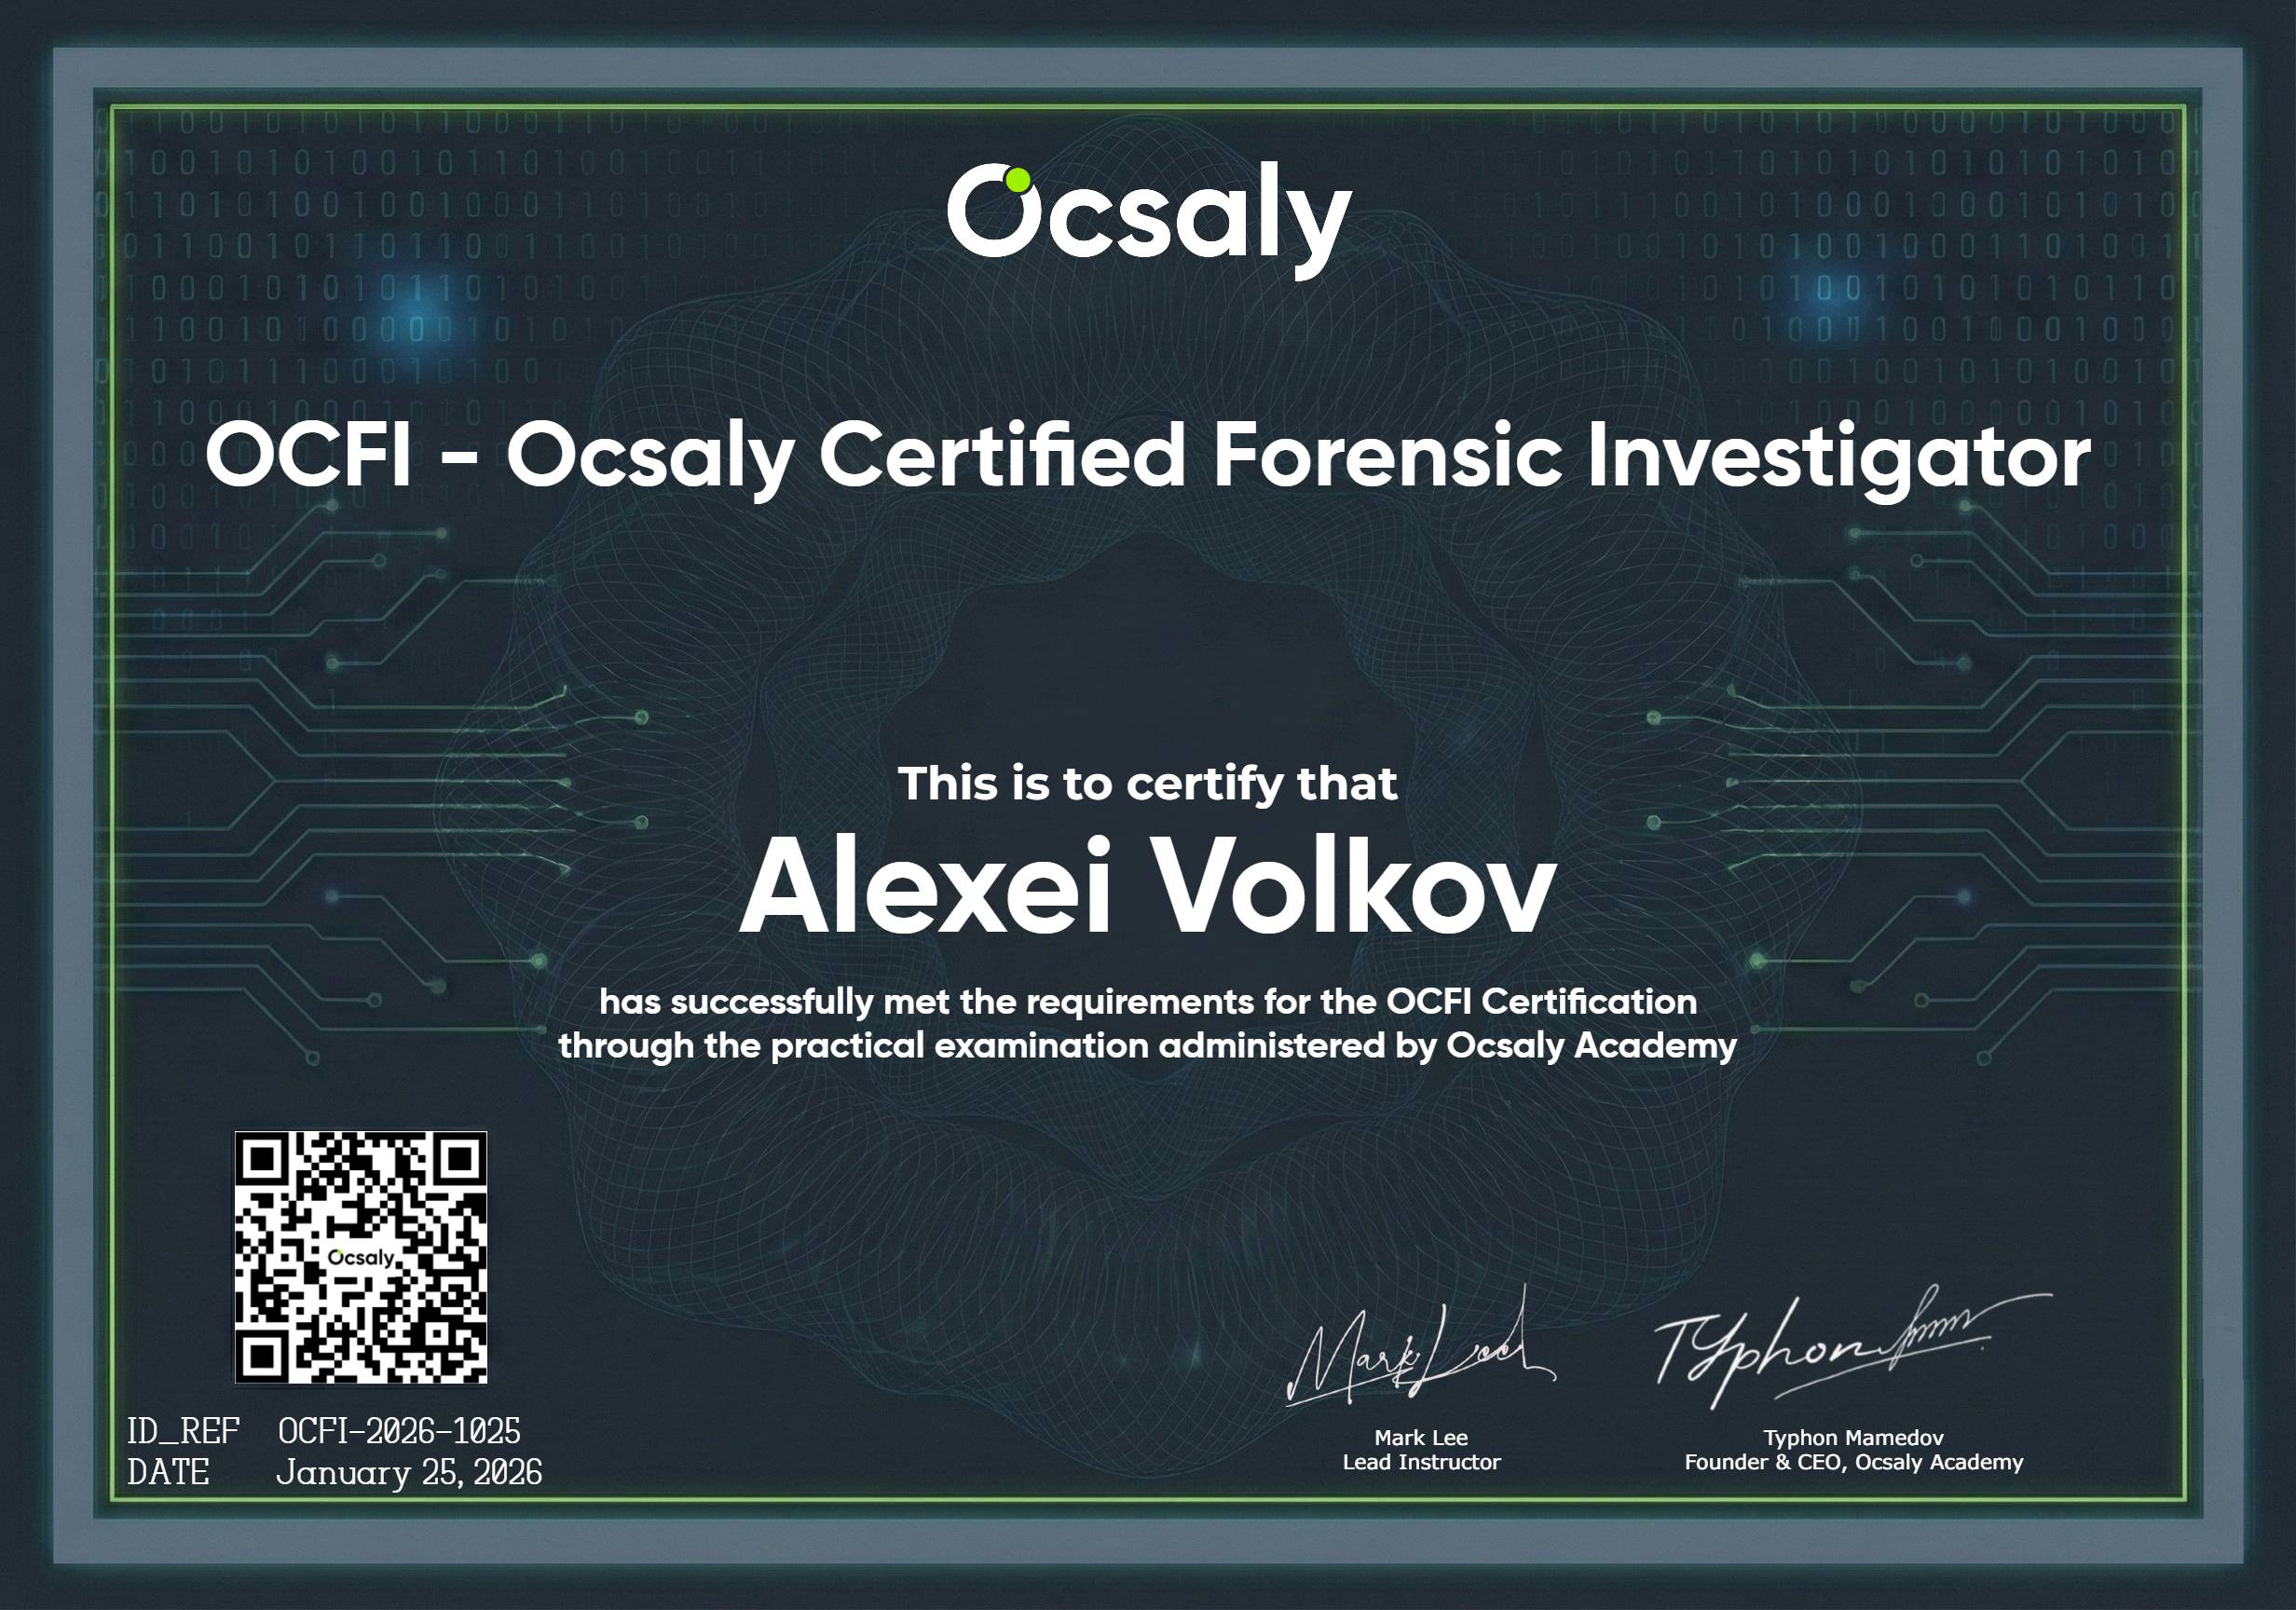
Ocsaly Certified Forensic Investigator
OPERATORS TRAINED : 580.000+
Master Professional Infrastructure Assessment Through Practical Execution.
Investigative Pipeline
Advanced Digital Forensic Certification Program (A-C)
Evidence Acquisition & Chain of Custody
The Core. Master the legal and technical protocols of evidence seizure. Dissect storage media, execute live RAM captures, and perform deep-dive file system analysis using Autopsy and Volatility Framework.
OS Forensics & File System Reconstruction
The Paper Trail. Reconstruct user activity by hunting for Registry artifacts, shell items, and browser traces. Move beyond the surface to extract hidden data from Windows, Linux, and macOS environments.
Mobile, Network & Cloud Forensics
The Modern Edge. Analyze PCAP data for lateral movement and extract encrypted application artifacts from mobile devices. Investigate Cloud Logs to reconstruct breaches in distributed infrastructures.
[ INVESTIGATIVE_CREDENTIAL ]
// FORENSIC_ENVIRONMENT_ACTIVE
[ INCLUDED_MODULES ]
-
✓ OCFI-A: Foundations & Acquisition30+ Hours ($199 Value)
-
✓ OCFI-B: OS Artifact Analysis45+ Hours ($199 Value)
-
✓ OCFI-C: Mobile & Network35+ Hours ($199 Value)
-
FINAL EXAM: 48h Practical Case
Professional Forensic Career Outcomes
Digital Forensic Lead
Lead deep-dive investigations into complex cyber crimes and corporate espionage cases.
Incident Response Specialist
Deploy to the frontlines of active breaches to contain threats and preserve critical evidence.
Cyber Crime Investigator
Partner with legal and law enforcement agencies to build ironclad digital cases for prosecution.
Investigative Validation
"The memory analysis framework in OCFI-A changed how I look at volatility. Capturing a live kernel state and extracting process hollowing artifacts felt like true digital detective work."
"Most forensic courses just teach you to run Autopsy. OCFI forces you to understand the hex. Recovering deleted NTFS MFT records manually gave me a massive edge in the field."
"The 48-hour exam is a masterpiece of stress. You aren't just finding flags; you're building a verifiable chain of custody for a mobile device that actually holds up to scrutiny."
"OCFI-B's deep dive into Registry forensics is clinical. I was able to timeline a persistent malware infection back to the exact second of the initial USB insertion."
"The network forensic modules are brutal. Reconstructing an entire exfiltration attempt from fragmented PCAPs was the most challenging thing I've done in my career."
"Ocsaly is the difference between a tool-user and a scientist. The focus on manual reconstruction over automated artifacts is why this is a true pro-grade certification."
Investigative Inventory & Certification
30+ HOURS
OCFI-A: FOUNDATIONS & ACQUISITION
PROTOCOLS: Chain of Custody, Order of Volatility, Legal Compliance, Evidence Handling, Integrity Hashing (MD5/SHA-256).
ACQUISITION: Live RAM Capture, Disk Imaging (E01/DD), Dead Box Forensics, Write-Blocker Implementation, Remote Imaging.
FRAMEWORKS: Autopsy Suite, Volatility Framework, FTK Imager, Magnet AXIOM Foundations, Hex Workshop, Data Carving.
45+ HOURS
OCFI-B: OS ARTIFACT ANALYSIS
WINDOWS: Registry Hive Analysis (RUN keys, SAM), Shellbags, LNK Files, Jump Lists, Prefetch, Event Logs (EVTX), Shadow Copies.
UNIX/MAC: Plist Analysis, Bash History, System Logs, File System Events (FSEvents), Unified Logging, Permission Persistence.
TIMELINING: Super-timeline Generation, Artifact Correlation, User Activity Reconstruction, Persistence Mechanism Detection.
35+ HOURS
OCFI-C: MOBILE & NETWORK FORENSICS
MOBILE: iOS/Android Physical & Logical Extraction, SQLite Database Querying, Encrypted App Recovery (Signal/WhatsApp).
NETWORK: PCAP Deep Packet Inspection, Lateral Movement Reconstruction, DNS Cache Exfiltration, Proxy Logs, TLS Interception.
INCIDENT: Ransomware Artifact Recovery, Lateral Movement Tracking, Command & Control (C2) Identification.
OCFI INVESTIGATOR CERTIFICATION & EXAM
EXAM: 48-Hour Hands-On Practical Examination. Candidates must reconstruct a multi-stage breach and present a Court-Ready Forensic Report.
CREDENTIAL: Cryptographically Verified Investigator Status, Permanent ID on Global Registry, Professional Case Credentials.
RESOURCES: Premium Forensic Lab Access, Reusable Investigation Checklists, Courtroom Testimony Guide.
[ SPECIALIZATION_AUTHORIZATION ]
- ✓ Lifetime Access to All 3 Modules
- ✓ Evidence Case Files & Lab Access
- ✓ Official 48h Practical Exam Attempt
- ✓ Court-Ready Reporting Templates
// SECURE CASE FILE ENCRYPTION ACTIVE
THE INVESTIGATOR STANDARD
The OCFI is not a participatory award. It is a forensic-grade credential earned through the methodical reconstruction of digital evidence. When you hold this ID, you carry a verified history of Investigative Precision.
Analysis is the process. The report is the proof.
Welcome to the Academy.
Investigative FAQs
Jurisdictional Integration
OCFI Investigators are currently active and validated within the following high-stakes forensic environments:
Investigative Requirements
| COMPONENT | MINIMUM SPECIFICATION | RECOMMENDED PROFILE |
|---|---|---|
| Operating System | Win10+ or Linux (SANS SIFT/CSI) | Dedicated Forensic Workstation VM |
| Hardware (RAM) | 8GB Total System RAM | 32GB+ Optimized for Evidence Parsing |
| CPU Logic | Hex-Core 2.5GHz+ | Octa-Core+ x64 Forensic Architecture |
| Connectivity | 10Mbps (Secure VPN Access) | 50Mbps+ (Low Latency Evidence Sync) |
If the technical depth of the OCFI does not meet the investigative standards outlined in this dossier within 7 days, we provide a no-friction tuition reversal. We only train those who find value in our forensic logic.
Curriculum Valuation
// LIFETIME ACCESS. 48H PRACTICAL EXAM. EVIDENCE LABS INCLUDED.
